
UserLink API Reference
Atomic's API is built around RESTful principles, using JSON encoded request and response bodies.
To get going quickly, we recommend using Postman - an API collaboration tool. Atomic provides a public workspace which you can fork into your own workspace. Use the button below to get started.
The workspace comes fully documented with:
- several useful flows using our APIs
- requests for all of the Atomic endpoints
- an environment containing placeholders for all the variables needed to connect to your Sandbox instance of Console
Authentication
Atomic uses a combination of API keys and access tokens to authenticate requests. Your API keys carry many privileges, so be sure to keep them secure! Do not share your secret API keys in publicly accessible areas such as GitHub, client-side code, etc.
API Key and Secret
You can retrieve and manage your API key and secrets on the credentials page on the Atomic Console. Include these headers in requests that are secured with your API Key and Secret:
401 and error code 40111 (Invalid IP address.). Contact your Atomic representative to set up or change the list. | Header | Description |
|---|---|
x-api-key | API Key for your Atomic account |
x-api-secret | API Secret for your Atomic account |
Access Token
A publicToken will be included in the headers of requests which are made via the end user from client-side code, e.g. searching for their employer or initializing a Task. The publicToken defaults to a 24 hour expiry, but can be set to a minimum of 30 minutes or a maximum of 30 days by passing in the desired duration using the optional tokenLifetime property in the call to /access-token. The minimum is to allow for users to complete variations of the flows, such as MFA, which can take time.
| Header | Description |
|---|---|
x-public-token | Public token generated during access token creation. |
Mutual TLS
Optionally, Atomic can require a client certificate on connections from your servers. Requests using mutual TLS go to a dedicated hostname per environment and still carry the API Key and Secret headers above. Endpoints routed through Atomic's PCI Card Data Environment do not support mutual TLS. See the Mutual TLS for API Requests guide for requirements and setup.
Request Body Encryption
Optionally, the JSON body of a request authenticated with your API Key and Secret can be encrypted as a JWE using a public key Atomic publishes for your account. Send the encrypted payload as { "encryptedBody": "..." } and include the header below. See the Request Body Encryption guide for details.
| Header | Description |
|---|---|
x-enc-key-id | The _id of the public key used to encrypt the body, from Get JWE Public Keys. |
Errors
Our API returns standard HTTP success or error status codes. For errors, we will also include extra information about what went wrong encoded in the response as JSON. The various HTTP status codes we might return are listed below.
| Code | Title | Description |
|---|---|---|
| 200 | OK | The request was successful. |
| 400 | Bad Request | The request was unacceptable. This includes request bodies or parameters that fail validation (message Invalid request payload, with details in data.errors) and requests that reference a user or other resource that does not exist (for example User not found.). |
| 401 | Unauthorized | Missing or invalid credentials. See Authentication errors below. |
| 403 | Forbidden | Your credentials are valid, but the endpoint is not enabled for your account, or the public token used does not belong to the user named in the request. |
| 404 | Not Found | The URL does not match any endpoint. Check the path and HTTP method. A user or resource that cannot be found returns 400, not 404. |
| 422 | Unprocessable Entity | The requested product is not supported by this endpoint. |
| 429 | Too Many Requests | Too many requests, please try again later. |
| 50X | Internal Server Error | An error occurred with our API. |
Error response body
Every error response uses the same JSON shape. message is a human-readable summary. code is a numeric Atomic error code whose first three digits match the HTTP status; it is present on most errors but omitted on schema validation failures. type names the kind of error, and data carries additional detail when there is any. Validation failures include data.errors, a list of readable messages, and data.verboseErrors, the raw output of the schema validator.
{
  "type": "BadRequestError",
  "message": "Invalid request payload",
  "data": {
    "errors": [
      "must have required property 'identifier'"
    ],
    "verboseErrors": [
      {
        "instancePath": "",
        "schemaPath": "#/required",
        "keyword": "required",
        "params": {
          "missingProperty": "identifier"
        },
        "message": "must have required property 'identifier'"
      }
    ]
  }
}{
"type": "ClientError",
"message": "User not found.",
"code": 40011
}Authentication errors
A 401 response includes a code that identifies the cause. The most common are listed below.
| Code | Message | Cause |
|---|---|---|
| 40101 | Unauthorized. | The API key or secret is not valid. |
| 40103 | Expired. | The public token has expired. Create a new access token. |
| 40104 | Invalid token. | The public token is not recognized or has been revoked. |
| 40106 | Authentication has not been configured for this endpoint. | No credentials were sent, or the credentials sent are not the kind this endpoint accepts. Most often this means a x-public-token header was sent to an endpoint that requires x-api-key and x-api-secret, or the other way around. Check the authentication listed for the endpoint. |
| 40111 | Invalid IP address. | IP allowlisting is enabled for your account and the request came from an address that is not on the list. |
Access Token
An AccessToken grants access to Atomic's API resources for an end user when its value is used as the x-public-token header.
Create Access Token
Authentication is handled via the API Key and Secret method. This API is intended to be called from your backend service so your API Keys and Secrets are not deployed to your client side application.
Required Properties
identifierstring- A unique identifier from your system that will be used to reference this user. This could be a primary key used in your system or another unique identifier. Creating multiple access tokens with the same identifier will tie those tokens to the same user in Atomic's system.
POST/access-token{
"identifier": "YOUR_INTERNAL_IDENTIFIER"
}Product Specific Properties
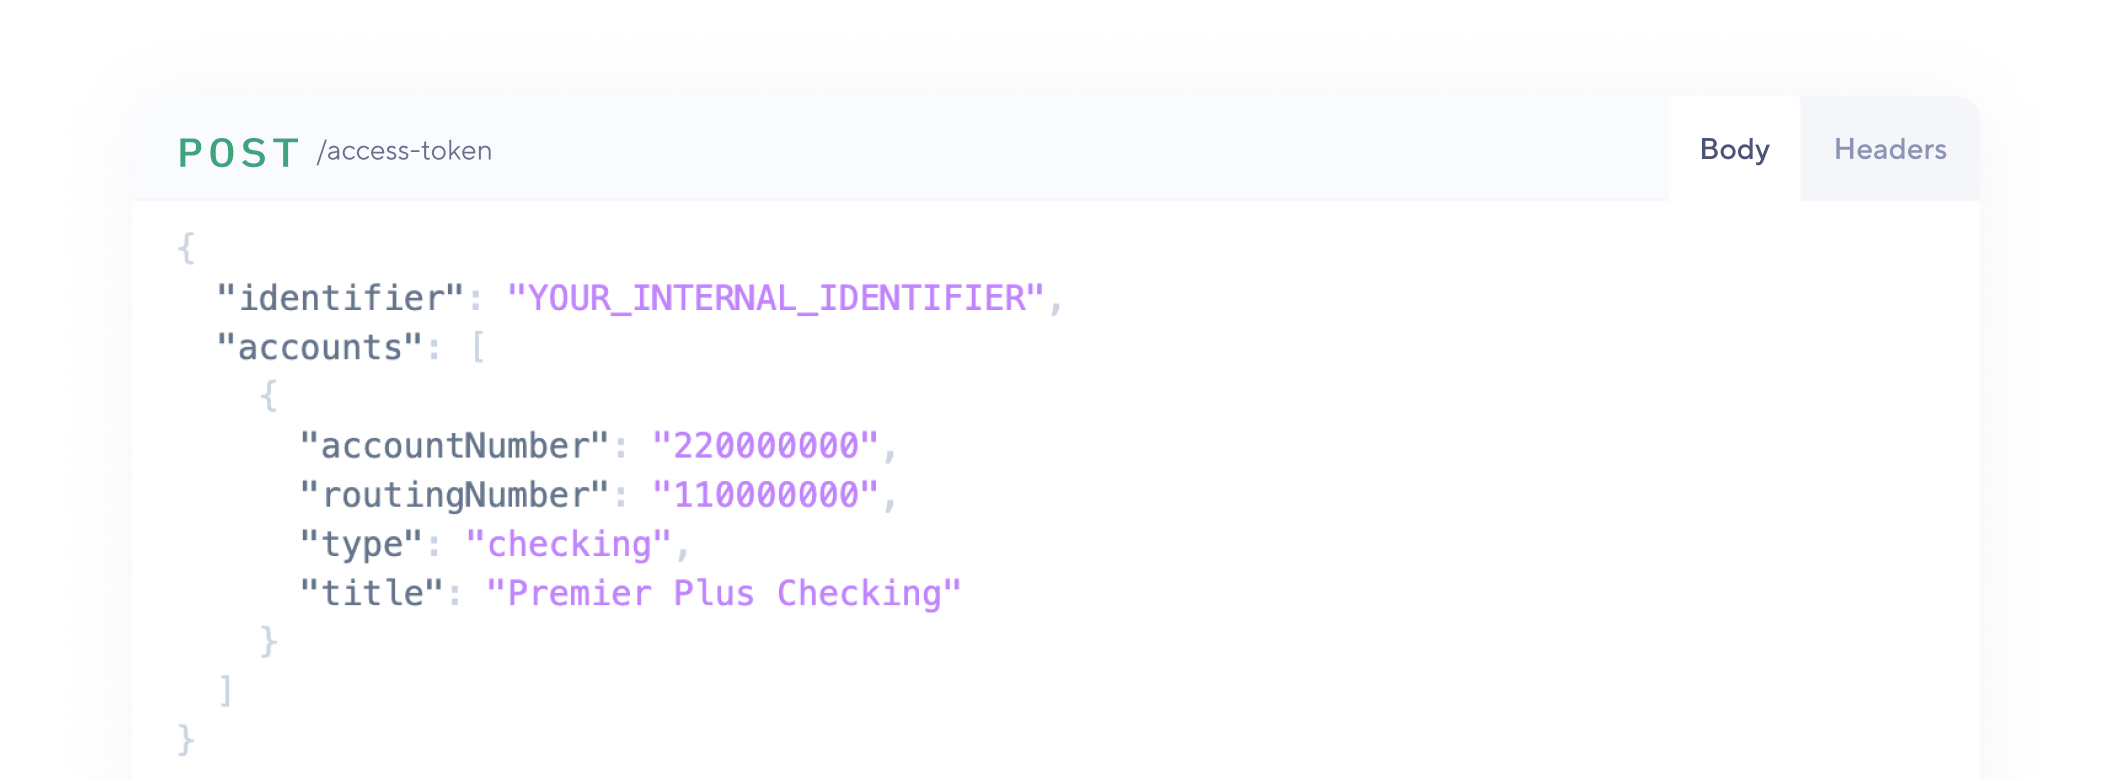
The identifier property is required for generating all AccessTokens, but each Atomic product may require some additional context in order to correctly set up the flow in our backend. Please refer to the implementation pages for each Product to get specific details regarding AccessToken creation.


{
  "data": {
    "publicToken": "PUBLIC_TOKEN"
  }
}
Revoke Access Token
This endpoint is used to revoke an existing AccessToken. This action invalidates the token, preventing it from being used to access Atomic's API resources.
Authentication is handled via the API Key and Secret method. This API is intended to be called from your backend service so your API Keys and Secrets are not deployed to your client side application.
PUT/access-token/:publicToken/revokex-api-keyAPI Key for your Atomic account
x-api-secretAPI Secret for your Atomic account
CoAuth
Atomic has established direct partnerships with select payroll systems to enable seamless user lookups, a capability branded as CoAuth.
By identifying a user and leveraging the payroll system’s stored multi-factor authentication (MFA) flow, Atomic can securely verify the user’s identity. Once verified, the payroll system provides the necessary access for Atomic to update the user’s direct deposit information efficiently; reducing friction, enhancing conversion rates, and overall improving the user experience.
Pre-screen
The Pre-Screen API allows for pre-screening a user through CoAuth by using their identity data to perform a lookup within supported payroll systems. This API is typically called after the user expresses intent to set up direct deposit but before launching them into Transact.
Once the user is identified within a payroll system, Atomic can seamlessly set up direct deposit on their behalf, improving conversion rates and creating a more streamlined user experience.
Authentication is handled via the API Key and Secret method. This API is intended to be called from your backend service so your API Keys and Secrets are not deployed to your client side application.
Required Properties
identifierstring- The user's unique identifier, to be used again during AccessToken creation.
Optional Properties
identityobject
incomeSources array is returned.POST/pre-screen{
"identifier": "END_USER_IDENTIFIER",
"identity": {
"ssn": "666-00-9876",
"dateOfBirth": "1980-01-01",
"phone": "555-867-5309",
"email": "test@example.com"
}
}Response
A successful pre-screen will return a data object containing an incomeSources array. Each object in the array will contain details about the payroll system where the user was verified and a data object with specifics regarding the lookup operation. The array is empty when the user was not found in any supported payroll system.
incomeSources[IncomeSource]- An array of IncomeSource objects containing details of the lookups performed by Atomic in the CoAuth enabled payroll systems.
Child Properties
Required Properties
dataobject- An object with details about the lookup operation in the payroll system.
Child Properties
Required Properties
userStatusenum- The status of the lookup. Options are:
VERIFIED_PAYROLLNOT_FOUNDUNSUPPORTED_PAYROLL originenum- The origin of the income source verification. Currently limited to
pre-screen. lookupDatestring- The timestamp of when the income source was derived or verified. Returned in ISO 8601 format.
{
  "success": true,
  "data": {
    "incomeSources": [
      {
        "data": {
          "userStatus": "VERIFIED_PAYROLL",
          "origin": "pre-screen",
          "lookupDate": "2024-08-27T16:44:21.482Z"
        },
        "company": {
          "_id": "5d38f1e8512bbf71fb776015",
          "name": "ADP",
          "branding": {
            "logo": {
              "url": "https://atomicfi-public-production.s3.amazonaws.com/a8d7e778-b718-45e0-b639-2305e33e7f95_ADP.png",
              "backgroundColor": "#F2F2F2"
            },
            "color": "#9460FE"
          }
        },
        "connector": {
          "_id": "5d38f1e8512bbf71fb776016",
          "name": "ADP",
          "branding": {
            "logo": {
              "url": "https://atomicfi-public-production.s3.amazonaws.com/a8d7e778-b718-45e0-b639-2305e33e7f95_ADP.png",
              "backgroundColor": "#F2F2F2"
            },
            "color": "#9460FE"
          }
        }
      }
    ]
  }
}
Company
A user has the option to link their payroll through their payroll provider or by navigating our employer-to-payroll system mapping. We have the notion of a Company that encompasses both aspects.
Company Search
Use this endpoint to build a typeahead experience, as employed in our Transact SDK, or to get the company's _id for deeplinking to the login section of Transact.
Search for a Company using a text query. Searches can also be filtered by passing in additional properties detailed below.
Use this lookup when you need to identify a payroll provider. If you need additional metadata for a specific result, use the returned _id with Company Details.
Authentication can be handled via either the API Key and Secret method or the Access Token method.
Required Properties
querystring- Filters companies by name. Uses fuzzy matching to narrow results. Maximum length is 50 characters.
Optional Properties
scopes[string]
product and products properties. Options are: pay-linkuser-linkcustomproductstring
deposit, verify, and tax.products[string]
deposit, verify, and tax.tags[string]
gig-economy, payroll-provider, and unemployment.excludedTags[string]
gig-economy, payroll-provider, and unemployment.franchiseParentstring
_id of a franchise parent company. Restricts results to that brand’s franchisees, for building a franchise location picker. query is still required.POST/company/search{
"query": "Doordash",
"product": "deposit"
}Response
Successfully querying the Company search endpoint will return a payload with a data array of Company objects.
under-maintenance, the affected products and actions will be listed in the response field, underMaintenanceProductsAndActions. Users will be unable to initiate authentication for the respective product or action until it has been restored. _idstring- Unique identifier for the company.
namestring- Company name.
statusstring- Possible values include
operationalorunder-maintenance. connector.availableProducts[string]- A list of compatible products.
connector.capabilities.supportedPaymentMethods[string]- When present, shows the supported payment method types for the connector (
card,bank). Often omitted for deposit-only connectors. branding.logo.urlstring- Logo for the company, in PNG format.
branding.colorstring- Branding color for the company.
tags[string]- Tags with which a company is associated. Possible values include
gig-economy,payroll-provider,unemployment, andmanual-deposits. underMaintenanceProductsAndActions[string]Optional- A list of products and actions currently under maintenance for the company.
{
  "data": [
    {
      "_id": "5d38f1e8512bbf71fb776015",
      "name": "DoorDash",
      "status": "operational",
      "connector": {
        "_id": "5d38f182512bbf0c06776013",
        "availableProducts": [
          "deposit"
        ],
        "capabilities": {
          "distributionTypes": [
            "total"
          ]
        }
      },
      "branding": {
        "logo": {
          "url": "https://atomicfi-public-production.s3.amazonaws.com/a8d7e778-b718-45e0-b639-2305e33e7f95_ADP.svg",
          "backgroundColor": "#F2F2F2"
        },
        "color": "#9460FE"
      },
      "tags": [
        "gig-economy"
      ]
    }
  ]
}
Company List
Use this endpoint to retrieve the list of companies available to your account. It is well suited for building a static company catalog, pulling a snapshot of the catalog for design or planning workflows, or pre-validating which companies your customers can connect.
Results are sorted by popularity, with the most frequently selected companies appearing first. Popularity is based on how often users select each company in Transact over a rolling two-week window.
For typeahead-style lookup by name, use Company Search. For a single company by _id, use Company Details.
Authentication is handled via the API Key and Secret method. This API is intended to be called from your backend service so your API Keys and Secrets are not deployed to your client side application.
Optional Properties
These are query string parameters on the request URL (this endpoint is GET, so parameters are not sent as a JSON body). Pass a single value with product or scope to narrow the list.
Example: /company/list?scope=user-link&product=deposit
productenumOptional
deposit — /company/list?product=depositdepositscopeenumOptional
user-link — /company/list?scope=user-linkuser-linklimitnumberOptional
1 and 100. Defaults to 100.skipnumberOptional
0 or greater. Defaults to 0.GET/company/listx-api-keyAPI Key for your Atomic account
x-api-secretAPI Secret for your Atomic account
Response
A successful response returns a payload with a data array of Company objects.
under-maintenance, the affected products and actions will be listed in the response field, underMaintenanceProductsAndActions. Users will be unable to initiate authentication for the respective product or action until it has been restored. When a connector defines Pay Link payment methods, each item also includes connector.capabilities.supportedPaymentMethods (for example card or bank). Many deposit-only connectors omit this field.
data[object]- Array of company objects matching the request filters.
_idstring- Unique identifier for the company.
namestring- Company name.
branding.logo.urlstring- Logo for the company, in PNG format.
branding.colorstring- Branding color for the company.
tags[string]- Tags with which a company is associated. Possible values include
gig-economy,payroll-provider,unemployment, andmanual-deposits. connector.availableProducts[string]- A list of compatible products.
connector.capabilities.supportedPaymentMethods[string]- When present, shows the supported payment method types for the connector (
card,bank). Often omitted for deposit-only connectors. statusstring- Possible values include
operational,under-maintenance, anddisabled. underMaintenanceProductsAndActions[string]Optional- A list of products and actions currently under maintenance for the company.
{
  "success": true,
  "data": [
    {
      "_id": "5d38f1e8512bbf71fb776015",
      "name": "DoorDash",
      "status": "operational",
      "createdAt": "2019-07-24T18:03:20.184Z",
      "tags": [
        "gig-economy"
      ],
      "branding": {
        "logo": {
          "url": "https://atomicfi-public-production.s3.amazonaws.com/a8d7e778-b718-45e0-b639-2305e33e7f95_doordash.svg",
          "backgroundColor": "#FF3008"
        },
        "color": "#FF3008"
      },
      "connector": {
        "_id": "5d38f182512bbf0c06776013",
        "availableProducts": [
          "deposit"
        ],
        "capabilities": {
          "distributionTypes": [
            "total"
          ]
        }
      },
      "alternativeConnectors": [],
      "coAuthConnectors": [],
      "availableProducts": [
        "deposit"
      ],
      "availableActions": []
    },
    {
      "_id": "5fc810d63279fe0009c493ec",
      "name": "Paychex Flex",
      "status": "operational",
      "createdAt": "2020-12-02T22:10:30.966Z",
      "tags": [
        "payroll-provider"
      ],
      "branding": {
        "logo": {
          "url": "https://cdn-public.atomicfi.com/9d736728-7ac7-46f6-b559-ddc711a9253b_paychex.png",
          "backgroundColor": "#004B8D"
        },
        "color": "#004B8D"
      },
      "connector": {
        "_id": "5f516d0ad5e724000712f154",
        "availableProducts": [
          "deposit"
        ],
        "capabilities": {
          "distributionTypes": [
            "total",
            "fixed",
            "percent"
          ]
        }
      },
      "alternativeConnectors": [],
      "coAuthConnectors": [],
      "availableProducts": [
        "deposit"
      ],
      "availableActions": []
    }
  ]
}
Company Details
Use this endpoint to retrieve all information Atomic has for a specific company.
The response includes company metadata such as branding, status, search information, and connector capabilities.
This can be useful when you need to render payroll provider branding in your own UI, confirm whether a company supports direct deposit-related flows before deeplinking, or inspect connector capabilities such as supported distribution actions, distribution types, and authentication methods.
Authentication is handled via the API Key and Secret method. This API is intended to be called from your backend service so your API Keys and Secrets are not deployed to your client side application.
GET/company/:companyId/detailsx-api-keyAPI Key for your Atomic account
x-api-secretAPI Secret for your Atomic account
Response
A successful request returns the public company details payload for the specified company, including status, search metadata, connector capabilities, supported products, and payroll-provider branding details.
under-maintenance, the affected products and actions will be listed in the response field, underMaintenanceProductsAndActions. Users will be unable to initiate authentication for the respective product or action until it has been restored. _idstring- Unique identifier for the company.
namestring- Company name.
subtextstring- Optional descriptive text shown alongside the company name.
createdAtstring- Timestamp for when the company record was created.
brandingobject- Branding metadata for the company.
tags[string]- Company tags associated with the payroll provider.
statusstring- Possible values include
operational,under-maintenance, anddisabled. searchstring- Search text used to match the company in company lookup flows.
keywords[string]- Supplemental search keywords associated with the company.
isConfigurableConnectorboolean- Indicates whether the selected connector can be configured.
alternativeConnectors[]- Alternative connector options available for the company, if any.
coAuthConnectors[]- Co-auth connector options available for the company, if any.
franchiseParentobject- Metadata for the franchise parent company when this company is a franchise child.
availableProducts[string]- Products that can be launched with this company.
connectorobject- Connector metadata for this company.
Child Properties
Optional Properties
_idstringUnique identifier for the connector.namestringDisplay name for the connector.createdAtstringTimestamp for when the connector record was created.brandingobjectBranding metadata for the connector.availableProducts[string]Products that can be launched with this connector.capabilitiesobjectConnector capabilities exposed by the public API.Child Properties
Optional Properties
headlessAuthenticationbooleanWhether the connector supports headless authentication.ssoAuthenticationbooleanWhether the connector supports SSO authentication.distributionActions[string]Distribution actions supported by the connector, such as creating a new deposit allocation.distributionTypes[string]Distribution types supported by the connector, such astotal,fixed, orpercent.authenticationMethods[string]Authentication methods supported by the connector.showConfirmDistributionPagebooleanWhether the connector shows a distribution confirmation page before submitting changes. underMaintenanceProductsAndActions[string]Optional- A list of products and actions currently under maintenance for the company.
{
  "success": true,
  "data": {
    "_id": "5fc810d63279fe0009c493ec",
    "createdAt": "2020-12-02T22:10:30.966Z",
    "branding": {
      "logo": {
        "url": "https://cdn-public.atomicfi.com/9d736728-7ac7-46f6-b559-ddc711a9253b_paychex.png",
        "backgroundColor": "#004B8D"
      },
      "color": "#004B8D"
    },
    "name": "Paychex Flex",
    "subtext": "",
    "tags": [
      "payroll-provider",
      "us-incorporated"
    ],
    "alternativeConnectors": [],
    "isConfigurableConnector": false,
    "coAuthConnectors": [],
    "search": "paychex flex",
    "keywords": [],
    "connector": {
      "_id": "5f516d0ad5e724000712f154",
      "branding": {
        "logo": {
          "url": "https://cdn-public.atomicfi.com/9d736728-7ac7-46f6-b559-ddc711a9253b_paychex.png",
          "backgroundColor": "#004B8D"
        },
        "color": "#004B8D"
      },
      "name": "Paychex Flex",
      "createdAt": "2020-09-03T22:24:10.729Z",
      "availableProducts": [
        "deposit"
      ],
      "capabilities": {
        "headlessAuthentication": true,
        "ssoAuthentication": false,
        "distributionActions": [
          "create"
        ],
        "distributionTypes": [
          "total",
          "fixed",
          "percent"
        ],
        "authenticationMethods": [
          "standard-auth",
          "true-auth",
          "true-auth-desktop"
        ],
        "showConfirmDistributionPage": true
      }
    },
    "status": "operational",
    "availableProducts": [
      "deposit"
    ]
  }
}
Task
Each discrete payroll operation, such as a verification of income, direct deposit switch, or update to a payment account of file, will instantiate what is referred to as a Task in our system. A Task consists of an authentication step where Atomic logs into a payroll or service provider and an operation step where we read data or write to the system; either a direct deposit allocation or updating a payment account on file, depending on the Task.
Get Task Details
This endpoint returns the details of a Task. Submit the corresponding taskId and receive the details of that Task.
Authentication is handled via the API Key and Secret method. This API is intended to be called from your backend service so your API Keys and Secrets are not deployed to your client side application.
Required Properties
taskIdstring- The id of the Task. The
taskIdproperty is sent in multiple webhooks or any of the interaction events which are fired after the authentication phase of the flow has begun.
GET/task/:taskId/detailsx-api-keyAPI Key for your Atomic account
x-api-secretAPI Secret for your Atomic account
Response
A successful request will return the details of the task.
_idstring- The id of the task.
authenticatedboolean- Indicates whether or not the task has successfully authenticated against the payroll system.
companyobject- Metadata for the employer.
Child Properties
connectorobject- Metadata for the connector.
Child Properties
createdAtdate- The timestamp when the task was created, stored in UTC and ISO 8601 format.
updatedAtdate- The timestamp when the task was last updated, stored in UTC and ISO 8601 format.
depositDataobjectOptional- If the task is a deposit task, this data will indicate the type of deposit switch performed.
Child Properties
Optional Properties
accountTypestringThe type of the account. Possible values includesavings,checking, orpaycard.distributionAmountnumberThe amount being distributed to the account. WhendistributionTypeispercent, the number represents a percentage of the total pay. WhendistributionTypeisfixed, this number represents a fixed dollar amount. This value is not set whendistributionTypeistotal.distributionTypestringThe type of distribution for the account. Possible values includetotal,percent, orfixed.lastFourAccountNumberstringThe last four digits of the account number. If your account is configured to receive full account information, this field is replaced byaccountNumber, containing the full account number.routingNumberstringThe routing number.titlestringThe title of the account. failReasonstringOptional- The failure reason associated with a failed task. Will consist of one of the failure values.
linkedAccountstringOptional- The id of the linked account used to create the task.
metadataobjectOptional- The
metadataprovided by your system when the task was initialized. payrollDataAvailableboolean- A boolean value indicating whether or not the user's payroll data is ready for retrieval via api.
productstring- The product of the task. Possible values include
deposit,verify, andtax. statusstring- The status of the task which may be
queued,processing,failed, orcompleted.. Other transitional values may appear while a task is being processed; treat any value other thancompletedorfailedas in progress. taskWorkflowobject- The Task Workflow of the Task. When multiple tasks are associated with a single workflow, they will all have the same
taskWorkflowobject. Every Task is associated with a Task Workflow, even if it not associated with another Task. userobject- The user who processed the Task.
Child Properties
Required Properties
_idstring- The id of the user in atomic's system.
identifierstring- The user's unique identifier, as sent to Atomic during AccessToken creation.
{
  "data": {
    "task": {
      "_id": "65b15fd99b3f03aa9edff9de",
      "authenticated": true,
      "company": {
        "_id": "607e249736b9f053b536bde0",
        "branding": {
          "logo": {
            "url": "https://cdn-public.atomicfi.com/b02670fa-ce1b-4171-855b-6856b37bb938.png"
          }
        },
        "name": "Test Company"
      },
      "connector": {
        "_id": "607e249736b9f053b536bde1",
        "branding": {
          "logo": {
            "url": "https://cdn-public.atomicfi.com/b02670fa-ce1b-4171-855b-6856b37bb938.png"
          }
        },
        "name": "Test Connector"
      },
      "createdAt": "2024-01-01T00:00:00.000Z",
      "updatedAt": "2024-01-01T00:00:05.000Z",
      "depositData": {
        "accountType": "checking",
        "distributionAmount": 10,
        "distributionType": "fixed",
        "lastFourAccountNumber": "0000",
        "routingNumber": "22000000",
        "title": "Checking Account"
      },
      "failReason": "unknown-failure",
      "linkedAccount": "645963a0b754649972f3d4ac",
      "metadata": {
        "data": "test"
      },
      "payrollDataAvailable": false,
      "product": "deposit",
      "status": "failed",
      "taskWorkflow": {
        "_id": "643f2ed34253e21bdbd2de31"
      },
      "user": {
        "_id": "607e249736b9f053b536bdea",
        "identifier": "GUID"
      }
    }
  }
}
Get Task Status
Calling this API returns the status of a Task. Submit the corresponding taskId and receive the status of that Task. For verify Tasks, the response also includes payrollDataAvailable, which indicates that any fetchable data is ready to be pulled via the corresponding API calls.
This endpoint is designed to be lightweight and intended for polling use cases.
Authentication is handled via the API Key and Secret method. This API is intended to be called from your backend service so your API Keys and Secrets are not deployed to your client side application.
Required Properties
taskIdstring- The id of the Task. The
taskIdproperty is sent in multiple webhooks or any of the interaction events which are fired after the authentication phase of the flow has begun.
GET/task/:taskId/statusx-api-keyAPI Key for your Atomic account
x-api-secretAPI Secret for your Atomic account
Response
A successful request will return the createdAt date, status, and if a Task failed (Tasks with a status of "failed") a failReason.
createdAtdate- The timestamp when the Task was created, stored in UTC and ISO 8601 format.
statusstring- The status of the task which may be
queued,processing,failed, orcompleted.. Other transitional values may appear while a task is being processed; treat any value other thancompletedorfailedas in progress. payrollDataAvailablebooleanOptional- A boolean value indicating whether or not the user's payroll data is ready for retrieval via api. Only returned for
verifyTasks. failReasonstringOptional- The failure reason associated with a failed task. Will consist of one of the failure values.
{
  "data": {
    "task": {
      "createdAt": "2023-01-03T16:40:48.009Z",
      "status": "completed",
      "payrollDataAvailable": true
    }
  }
}
Generate File URL
Generate a URL in order to download a user file (ex: paystubs PDFs). Each URL is valid for 1 hour.
Authentication is handled via the API Key and Secret method. This API is intended to be called from your backend service so your API Keys and Secrets are not deployed to your client side application.
Required Properties
taskIdstring- The
_idof the Task, which can be retrieved either from interaction events during the Transact session with the user or from the associated webhooks. fileIdstring- The
_idof the file. This is returned in API calls for relevant data categories, such as/taxesfor W-2's, or sent via relevant webhooks when a file is retrieved from the payroll system.
GET/task/:taskId/file/:fileId/generate-urlx-api-keyAPI Key for your Atomic account
x-api-secretAPI Secret for your Atomic account
{
  "url": "[ATOMIC-GENERATED-PRESIGNED-S3-URL]"
}PrescreenBeta
Prescreen is an endpoint you can call prior to task creation in order to get a predicted conversion confidence, offering additional insight into your user and the likelihood they will succeed using our service.
Authentication is handled via the API Key and Secret method. This API is intended to be called from your backend service so your API Keys and Secrets are not deployed to your client side application.
POST/task/prescreen{
"company": {
"name": "Amazon"
},
"product": "verify"
}Response
The response returns an object with a single confidence property as a string value. We will make this determination based on a variety of proprietary considerations such as traffic volumes and calculations with other similar connector types.
confidencestring- The likelihood of the user being successful using our flow. Will return a value of "HIGH" or "LOW".
{
  "data": {
    "confidence": "HIGH"
  }
}
Deposit Accounts
List deposit accounts once they've been synced to Atomic from the payroll provider.
For purely Deposit switch use cases, this information is not collected.
Authentication is handled via the API Key and Secret method. This API is intended to be called from your backend service so your API Keys and Secrets are not deployed to your client side application.
Required Properties
identifierstring- The user's unique identifier, as sent to Atomic during AccessToken creation.
Optional Properties
linkedAccountstring
_id of a LinkedAccount object provided as a query string parameter.taskstring
_id of the task, provided as a query string parameter, that was used to retrieve the data. If this parameter is not provided, the data that was most recently retrieved from the payroll system will be returned.includeOutputMetadatastring
true, the outputMetadata will be included in the response.GET/deposit-accounts/:identifierx-api-keyAPI Key for your Atomic account
x-api-secretAPI Secret for your Atomic account
Response
A successful response will return all direct deposit accounts on file for the user.
data[DepositAccounts]- An array of objects that include an array of deposit account objects,
company,connector,taskID, andlinkedAccountID if enabled.
{
  "data": [
    {
      "depositAccounts": [
        [
          {
            "routingNumber": "123123123",
            "accountNumber": "1122330000",
            "type": "checking",
            "bankName": "Molecular Bank",
            "distributionType": "percent",
            "distributionAmount": 80
          },
          {
            "routingNumber": "456456456",
            "accountNumber": "XXXX1111",
            "type": "savings",
            "bankName": "Molecular Bank",
            "distributionType": "percent",
            "distributionAmount": 20
          }
        ]
      ],
      "company": {
        "_id": "5d77f9e1070856f3828945c6",
        "name": "DoTerra",
        "branding": {
          "logo": {
            "_id": "5eb62781b4b83f0008f638cc",
            "url": "https://cdn.atomicfi.com/doterra-logo.svg"
          }
        }
      },
      "connector": {
        "_id": "5d77f95207085632a58945c3",
        "name": "ADP",
        "branding": {
          "logo": {
            "_id": "5eb62781b4b83f0008f6343c",
            "url": "https://cdn.atomicfi.com/adp-logo.svg"
          }
        }
      },
      "linkedAccount": "5f7212103a40e91f95ba376d",
      "task": "602414d84f9a1980cf5eafcc"
    }
  ]
}
Employment
Get employment data once its been synced to Atomic from the payroll provider.
For purely Deposit switch use cases, this information is not collected.
Authentication is handled via the API Key and Secret method. This API is intended to be called from your backend service so your API Keys and Secrets are not deployed to your client side application.
Required Properties
identifierstring- The user's unique identifier, as sent to Atomic during AccessToken creation.
Optional Properties
linkedAccountstring
_id of a LinkedAccount object provided as a query string parameter.taskstring
_id of the task, provided as a query string parameter, that was used to retrieve the data. If this parameter is not provided, the data that was most recently retrieved from the payroll system will be returned.includeOutputMetadatastring
true, the outputMetadata will be included in the response.GET/employment/:identifierx-api-keyAPI Key for your Atomic account
x-api-secretAPI Secret for your Atomic account
Response
A successful request will return the employment data for the user.
data[Employment]- An array of objects that include an employment object,
company,connector,taskID, andlinkedAccountID if enabled.
{
  "data": [
    {
      "employment": {
        "employeeType": "fulltime",
        "employmentStatus": "active",
        "jobTitle": "Product Manager",
        "startDate": "2017-04-19T12:00:00.000Z",
        "minimumMonthsOfEmployment": 58,
        "weeklyHours": 40,
        "employer": {
          "name": "Company Inc.",
          "address": {
            "line1": "12345 Enterprise Rd",
            "line2": "Suite 105",
            "city": "Salt Lake City",
            "state": "UT",
            "postalCode": "84111",
            "country": "USA"
          }
        }
      },
      "company": {
        "_id": "5d77f9e1070856f3828945c6",
        "name": "DoTerra",
        "branding": {
          "logo": {
            "_id": "5eb62781b4b83f0008f638cc",
            "url": "https://cdn.atomicfi.com/doterra-logo.svg"
          }
        }
      },
      "connector": {
        "_id": "5d77f95207085632a58945c3",
        "name": "ADP",
        "branding": {
          "logo": {
            "_id": "5eb62781b4b83f0008f6343c",
            "url": "https://cdn.atomicfi.com/adp-logo.svg"
          }
        }
      },
      "linkedAccount": "5f7212103a40e91f95ba376d",
      "task": "602414d84f9a1980cf5eafcc"
    }
  ]
}
Identity
Get identity data once its been synced to Atomic from the payroll provider.
For purely Deposit switch use cases, this information is not collected.
Authentication is handled via the API Key and Secret method. This API is intended to be called from your backend service so your API Keys and Secrets are not deployed to your client side application.
Required Properties
identifierstring- The user's unique identifier, as sent to Atomic during AccessToken creation.
Optional Properties
linkedAccountstring
_id of a LinkedAccount object provided as a query string parameter.taskstring
_id of the task, provided as a query string parameter, that was used to retrieve the data. If this parameter is not provided, the data that was most recently retrieved from the payroll system will be returned.includeOutputMetadatastring
true, the outputMetadata will be included in the response.GET/identity/:identifierx-api-keyAPI Key for your Atomic account
x-api-secretAPI Secret for your Atomic account
Response
A successful request will return the identity data for the user.
data[Identity]- An array of objects that include an identity object,
company,connector,taskID, andlinkedAccountID if enabled.
{
  "data": [
    {
      "identity": {
        "firstName": "Jane",
        "lastName": "Appleseed",
        "dateOfBirth": "1984-04-12T12:00:00.000Z",
        "email": "janeappleseed@example.com",
        "phone": "5558881111",
        "ssn": "111223333",
        "address": "123 Example St.",
        "city": "Salt Lake City",
        "state": "UT",
        "postalCode": "84111"
      },
      "company": {
        "_id": "5d77f9e1070856f3828945c6",
        "name": "DoTerra",
        "branding": {
          "logo": {
            "_id": "5eb62781b4b83f0008f638cc",
            "url": "https://cdn.atomicfi.com/doterra-logo.svg"
          }
        }
      },
      "connector": {
        "_id": "5d77f95207085632a58945c3",
        "name": "ADP",
        "branding": {
          "logo": {
            "_id": "5eb62781b4b83f0008f6343c",
            "url": "https://cdn.atomicfi.com/adp-logo.svg"
          }
        }
      },
      "linkedAccount": "5f7212103a40e91f95ba376d",
      "task": "602414d84f9a1980cf5eafcc"
    }
  ]
}
Income
Get income data once its been synced to Atomic from the payroll provider.
For purely Deposit switch use cases, this information is not collected.
Authentication is handled via the API Key and Secret method. This API is intended to be called from your backend service so your API Keys and Secrets are not deployed to your client side application.
Required Properties
identifierstring- The user's unique identifier, as sent to Atomic during AccessToken creation.
Optional Properties
linkedAccountstring
_id of a LinkedAccount object provided as a query string parameter.taskstring
_id of the task, provided as a query string parameter, that was used to retrieve the data. If this parameter is not provided, the data that was most recently retrieved from the payroll system will be returned.includeOutputMetadatastring
true, the outputMetadata will be included in the response.GET/income/:identifierx-api-keyAPI Key for your Atomic account
x-api-secretAPI Secret for your Atomic account
Response
A successful request will return the income data associated with the account.
data[Income]- An array of objects that include an income object,
company,connector,taskID, andlinkedAccountID if enabled.
{
  "data": [
    {
      "income": {
        "income": 45000,
        "incomeType": "yearly",
        "annualIncome": 45000,
        "hourlyIncome": 21.56,
        "netHourlyRate": 18.44,
        "payCycle": "weekly",
        "nextExpectedPayDate": "2020-06-30T12:00:00.000Z",
        "currentPayPeriodStart": "2020-06-13T12:00:00.000Z",
        "currentPayPeriodEnd": "2020-06-27T12:00:00.000Z",
        "unpaidHoursInPayPeriod": 24
      },
      "company": {
        "_id": "5d77f9e1070856f3828945c6",
        "name": "DoTerra",
        "branding": {
          "logo": {
            "_id": "5eb62781b4b83f0008f638cc",
            "url": "https://cdn.atomicfi.com/doterra-logo.svg"
          }
        }
      },
      "connector": {
        "_id": "5d77f95207085632a58945c3",
        "name": "ADP",
        "branding": {
          "logo": {
            "_id": "5eb62781b4b83f0008f6343c",
            "url": "https://cdn.atomicfi.com/adp-logo.svg"
          }
        }
      },
      "linkedAccount": "5f7212103a40e91f95ba376d",
      "task": "602414d84f9a1980cf5eafcc"
    }
  ]
}
Statements
Get statements data once its been synced to Atomic from the payroll provider.
For purely Deposit switch use cases, this information is not collected.
Authentication is handled via the API Key and Secret method. This API is intended to be called from your backend service so your API Keys and Secrets are not deployed to your client side application.
Required Properties
identifierstring- The user's unique identifier, as sent to Atomic during AccessToken creation.
Optional Properties
linkedAccountstring
_id of a LinkedAccount object provided as a query string parameter.taskstring
_id of the task, provided as a query string parameter, that was used to retrieve the data. If this parameter is not provided, the data that was most recently retrieved from the payroll system will be returned.includeOutputMetadatastring
true, the outputMetadata will be included in the response.limitstring
GET/statements/:identifierx-api-keyAPI Key for your Atomic account
x-api-secretAPI Secret for your Atomic account
Response
A successful request will return the statements for the user.
data[Statement]- An array of objects that include a statements object,
company,connector,taskID, andlinkedAccountID if enabled.
{
  "data": [
    {
      "statements": [
        {
          "date": "2020-06-15T12:00:00.000Z",
          "payPeriodStartDate": "2020-05-27T12:00:00.000Z",
          "payPeriodEndDate": "2020-06-12T12:00:00.000Z",
          "grossAmount": 1000,
          "ytdGrossAmount": 10000,
          "netAmount": 800,
          "ytdNetAmount": 8000,
          "paymentMethod": "deposit",
          "hours": 37,
          "deductions": [
            {
              "category": "taxes",
              "label": "Federal Income Tax",
              "rawLabel": "Federal Income Tax",
              "amount": 200,
              "ytdAmount": 2000
            },
            {
              "category": "taxes",
              "label": "State Income Tax",
              "rawLabel": "Utah State Tax",
              "amount": 50,
              "ytdAmount": 500
            },
            {
              "category": "other",
              "label": "Abc corp dd",
              "rawLabel": "Abc corp dd",
              "amount": 5,
              "ytdAmount": 50
            }
          ],
          "earnings": [
            {
              "category": "benefit",
              "rawLabel": "Social Security (Disability)",
              "amount": 1000
            },
            {
              "category": "bonus",
              "rawLabel": "Quarterly Bonus",
              "amount": 2000,
              "ytdAmount": 6000
            },
            {
              "category": "overtime",
              "rawLabel": "Overtime Pay",
              "amount": 100,
              "ytdAmount": 1000,
              "hours": 10,
              "rate": 15
            },
            {
              "category": "reimbursement",
              "rawLabel": "Gas Card",
              "amount": 25.47,
              "ytdAmount": 85.74
            }
          ],
          "netAmountAdjustments": [
            {
              "label": "Mileage Reimbursement",
              "amount": 25
            }
          ],
          "paystub": {
            "_id": "60abeff50836730008616fad",
            "url": "[ATOMIC-GENERATED-PRESIGNED-S3-URL]"
          },
          "parsedData": {
            "date": "2020-06-15T12:00:00.000Z",
            "payPeriodStartDate": "2020-05-27T12:00:00.000Z",
            "payPeriodEndDate": "2020-06-12T12:00:00.000Z",
            "grossAmount": 1000,
            "ytdGrossAmount": 10000,
            "netAmount": 800,
            "ytdNetAmount": 8000,
            "paymentMethod": "deposit",
            "hours": 37,
            "deductions": [
              {
                "category": "taxes",
                "rawLabel": "Federal Income Tax",
                "amount": 200,
                "ytdAmount": 2000
              },
              {
                "category": "taxes",
                "rawLabel": "Utah State Tax",
                "amount": 50,
                "ytdAmount": 500
              },
              {
                "category": "other",
                "rawLabel": "Abc corp dd",
                "amount": 5,
                "ytdAmount": 50
              }
            ],
            "earnings": [
              {
                "category": "benefit",
                "rawLabel": "Social Security (Disability)",
                "amount": 1000
              },
              {
                "category": "bonus",
                "rawLabel": "Quarterly Bonus",
                "amount": 2000,
                "ytdAmount": 6000
              },
              {
                "category": "overtime",
                "rawLabel": "Overtime Pay",
                "amount": 100,
                "ytdAmount": 1000,
                "hours": 10,
                "rate": 15
              },
              {
                "category": "reimbursement",
                "rawLabel": "Gas Card",
                "amount": 25.47,
                "ytdAmount": 85.74
              }
            ],
            "netAmountAdjustments": [
              {
                "rawLabel": "Mileage Reimbursement",
                "amount": 25
              }
            ]
          }
        },
        {
          "date": "2020-06-30T12:00:00.000Z",
          "payPeriodStartDate": "2020-05-27T12:00:00.000Z",
          "payPeriodEndDate": "2020-06-12T12:00:00.000Z",
          "grossAmount": 1000,
          "paymentMethod": "check",
          "hours": 34,
          "deductions": [
            {
              "category": "taxes",
              "label": "Federal Income Tax",
              "rawLabel": "Federal Income Tax",
              "amount": 200
            },
            {
              "category": "taxes",
              "label": "State Income Tax",
              "rawLabel": "Utah State Tax",
              "amount": 50
            },
            {
              "category": "other",
              "label": "Abc corp dd",
              "rawLabel": "Abc corp dd",
              "amount": 5
            }
          ],
          "paystub": {
            "_id": "60abeff50836730008616fae",
            "url": "[ATOMIC-GENERATED-PRESIGNED-S3-URL]"
          }
        }
      ],
      "company": {
        "_id": "5d77f9e1070856f3828945c6",
        "name": "DoTerra",
        "branding": {
          "logo": {
            "_id": "5eb62781b4b83f0008f638cc",
            "url": "https://cdn.atomicfi.com/doterra-logo.svg"
          }
        }
      },
      "connector": {
        "_id": "5d77f95207085632a58945c3",
        "name": "ADP",
        "branding": {
          "logo": {
            "_id": "5eb62781b4b83f0008f6343c",
            "url": "https://cdn.atomicfi.com/adp-logo.svg"
          }
        }
      },
      "linkedAccount": "5f7212103a40e91f95ba376d",
      "task": "602414d84f9a1980cf5eafcc"
    }
  ]
}
Timesheets
Get timesheets data once its been synced to Atomic from the payroll provider.
For purely Deposit switch use cases, this information is not collected.
Authentication is handled via the API Key and Secret method. This API is intended to be called from your backend service so your API Keys and Secrets are not deployed to your client side application.
Required Properties
identifierstring- The user's unique identifier, as sent to Atomic during AccessToken creation.
Optional Properties
linkedAccountstring
_id of a LinkedAccount object provided as a query string parameter.taskstring
_id of the task, provided as a query string parameter, that was used to retrieve the data. If this parameter is not provided, the data that was most recently retrieved from the payroll system will be returned.includeOutputMetadatastring
true, the outputMetadata will be included in the response.GET/timesheets/:identifierx-api-keyAPI Key for your Atomic account
x-api-secretAPI Secret for your Atomic account
Response
A successful request will return the timesheets for the user.
data[Timesheet]- An array of objects that include a timesheets object,
company,connector,taskID, andlinkedAccountID if enabled.
{
  "data": [
    {
      "timesheets": [
        {
          "duration": 420,
          "date": "2021-10-13T12:00:00.000Z",
          "type": "unpaid",
          "clockedIn": "2021-10-13T13:00:00.000Z",
          "clockedOut": "2021-10-13T20:00:00.000Z"
        },
        {
          "duration": 480,
          "date": "2021-10-12T12:00:00.000Z",
          "type": "paid",
          "clockedIn": "2021-10-12T13:00:00.000Z",
          "clockedOut": "2021-10-12T21:00:00.000Z"
        },
        {
          "duration": 340,
          "date": "2021-10-11T12:00:00.000Z",
          "type": "paid",
          "clockedIn": "2021-10-11T13:00:00.000Z",
          "clockedOut": "2021-10-11T18:40:00.000Z"
        }
      ],
      "company": {
        "_id": "5d77f9e1070856f3828945c6",
        "name": "DoTerra",
        "branding": {
          "logo": {
            "_id": "5eb62781b4b83f0008f638cc",
            "url": "https://cdn.atomicfi.com/doterra-logo.svg"
          }
        }
      },
      "connector": {
        "_id": "5d77f95207085632a58945c3",
        "name": "ADP",
        "branding": {
          "logo": {
            "_id": "5eb62781b4b83f0008f6343c",
            "url": "https://cdn.atomicfi.com/adp-logo.svg"
          }
        }
      },
      "linkedAccount": "5f7212103a40e91f95ba376d",
      "task": "602414d84f9a1980cf5eafcc"
    }
  ]
}
Taxes
Get tax data once its been synced to Atomic from the payroll provider.
For purely Deposit switch use cases, this information is not collected.
Authentication is handled via the API Key and Secret method. This API is intended to be called from your backend service so your API Keys and Secrets are not deployed to your client side application.
Required Properties
identifierstring- The user's unique identifier, as sent to Atomic during AccessToken creation.
Optional Properties
linkedAccountstring
_id of a LinkedAccount object provided as a query string parameter.taskstring
_id of the task, provided as a query string parameter, that was used to retrieve the data. If this parameter is not provided, the data that was most recently retrieved from the payroll system will be returned.typestring
w2 and 1040. If this parameter is not provided, all tax forms are returned.GET/taxes/:identifierx-api-keyAPI Key for your Atomic account
x-api-secretAPI Secret for your Atomic account
Response
A successful request will return the taxes for the user.
data[Tax]- An array of objects that include a array of taxes objects,
company,connector,taskID, andlinkedAccountID if enabled.
{
  "data": [
    {
      "taxes": [
        {
          "type": "w2",
          "year": "2020-01-01T00:00:00.000Z",
          "totalWages": 50000,
          "form": {
            "_id": "60abeff60836730008616faf",
            "url": "[ATOMIC-GENERATED-PRESIGNED-S3-URL]"
          },
          "parsedData": {
            "taxYear": 2022,
            "employeeTin": "XXX-XX-1234",
            "employerTin": "12-3456789",
            "employerNameAddress": {
              "name1": "Tax Form Issuer, Inc",
              "line1": "12021 Sunset Valley Dr",
              "line2": "Suite 230",
              "city": "Preston",
              "state": "VA",
              "postalCode": "20191"
            },
            "controlNumber": "012547 WY/OA7",
            "employeeName": {
              "first": "Kris",
              "last": "Public"
            },
            "employeeAddress": {
              "line1": "1 Main St",
              "line2": "Apartment 123",
              "city": "Melrose",
              "state": "NY",
              "postalCode": "12121"
            },
            "wages": 44416.74,
            "federalTaxWithheld": 6907.16,
            "socialSecurityWages": 47162.92,
            "socialSecurityTaxWithheld": 2924.1,
            "medicareWages": 47162.92,
            "medicareTaxWithheld": 683.86,
            "socialSecurityTips": 134.25,
            "allocatedTips": 149.75,
            "dependentCareBenefit": 543.25,
            "nonQualifiedPlan": 354.23,
            "codes": [
              {
                "code": "C",
                "amount": 301.5
              },
              {
                "code": "D",
                "amount": 2746.18
              },
              {
                "code": "DD",
                "amount": 4781.88
              }
            ],
            "other": [
              {
                "description": "Housing",
                "amount": 6500
              },
              {
                "description": "Union Dues",
                "amount": 1500
              }
            ],
            "statutory": false,
            "retirementPlan": true,
            "thirdPartySickPay": false,
            "stateTaxWithholding": [
              {
                "stateTaxWithheld": 1726.78,
                "state": "OH",
                "stateTaxId": "OH 036-133505158F-01",
                "stateIncome": 44416.74
              }
            ],
            "localTaxWithholding": [
              {
                "localTaxWithheld": 427.62,
                "localityName": "Kirtland",
                "state": "OH",
                "localIncome": 44416.74
              }
            ]
          }
        },
        {
          "type": "1099",
          "year": "2020-01-01T00:00:00.000Z",
          "form": {
            "_id": "60abeff60836730008616faf",
            "url": "[ATOMIC-GENERATED-PRESIGNED-S3-URL]"
          }
        }
      ],
      "company": {
        "_id": "5d77f9e1070856f3828945c6",
        "name": "DoTerra",
        "branding": {
          "logo": {
            "_id": "5eb62781b4b83f0008f638cc",
            "url": "https://cdn.atomicfi.com/doterra-logo.svg"
          }
        }
      },
      "connector": {
        "_id": "5d77f95207085632a58945c3",
        "name": "ADP",
        "branding": {
          "logo": {
            "_id": "5eb62781b4b83f0008f6343c",
            "url": "https://cdn.atomicfi.com/adp-logo.svg"
          }
        }
      },
      "linkedAccount": "5f7212103a40e91f95ba376d",
      "task": "602414d84f9a1980cf5eafcc"
    }
  ]
}
Linked Account
A LinkedAccount is a persistent connection that has been authenticated by an end-user. Once established, it can be used to perform read and write operations. Linked Accounts are the mechanism we use to facilitate our Continuous Access product. They are also used to initiate Task Workflows in the background.
List Linked Accounts
For a Continuous Access workflow, use this endpoint to list accounts linked to a particular user.
Authentication is handled via the API Key and Secret method. This API is intended to be called from your backend service so your API Keys and Secrets are not deployed to your client side application.
Required Properties
identifierstring- The user's identifier, as sent to Atomic during AccessToken creation. Passed with the URL as a path parameter (e.g.
/linked-account/list/:identifier), replacing:identifierwith your user'sidentifier.
GET/linked-account/list/:identifierx-api-keyAPI Key for your Atomic account
x-api-secretAPI Secret for your Atomic account
Response
The response contains an array of Linked Account objects for the end user.
_idstring- Unique identifier for the linked account.
validboolean- Whether or not the account credentials were valid after the last attempted use.
transactRequiredboolean- Whether or not using the account requires the user to be present within Transact.
lastSuccessstring- The datetime of the last successful usage of the account in ISO 8601 format.
lastFailurestring- The datetime of the last failed usage of the account in ISO 8601 format.
companyobject- The Company to which the account is linked.
connectorobject- The Connector to which the account is linked.
{
  "data": [
    {
      "_id": "5f7212103a40e91f95ba376d",
      "valid": true,
      "connector": {
        "_id": "5d77f95207085632a58945c3",
        "name": "ADP",
        "branding": {}
      },
      "company": {
        "_id": "5d77f9e1070856f3828945c6",
        "name": "DoTerra",
        "branding": {
          "logo": {
            "_id": "5eb62781b4b83f0008f638cc",
            "url": "https://cdn.atomicfi.com/logo.svg"
          }
        }
      },
      "lastSuccess": "2020-09-28T16:40:48.009Z",
      "transactRequired": false
    }
  ]
}
Use a Linked Account
Use this endpoint to initiate a Task Workflow in the background with a Linked Account. Send a request to this endpoint containing an array of the tasks you wish to execute and the _id of the LinkedAccount. This is generally used to refresh the data sync'ed to Atomic from a payroll system.
Authentication is handled via the API Key and Secret method. This API is intended to be called from your backend service so your API Keys and Secrets are not deployed to your client side application.
Required Properties
tasks[TaskConfiguration]- Defines configuration for the tasks you wish to execute as part of the task workflow.
Child Properties
Optional Properties
distributionobjectOptionally pass in enforced deposit settings.Child Properties
Optional Properties
typestringCan betotalto indicate the remaining balance of their paycheck,fixedto indicate a specific dollar amount, orpercentto indicate a percentage of their paycheck.amountnumberWhen
distribution.typeisfixed, it indicates a dollar amount to be used for the distribution. Whendistribution.typeispercent, it indicates a percentage of a paycheck. This is not required ifdistribution.typeistotal.actionstringThe change to make to the deposit allocation. Can becreateto add a new allocation,updateto modify an existing allocation, ordeleteto remove one.Default value: "create"
linkedAccountstring- The
_idof a LinkedAccount object.
POST/task-workflow/from-linked-account{
"tasks": [
{
"product": "verify"
}
],
"linkedAccount": "5f7212103a40e91f95ba376d"
}Response
Successfully creating a Task Workflow will return a payload with a data object containing metadata about the created taskWorkflow, its first task, and the associated company. The Task List in the Atomic Console can be used to track task progress.
Subsequent Tasks after the task referenced in the response will be processed as needed depending on the results of the first Task as well as the configuration provided; their progress may be tracked via webhooks. If you plan on implementing webhooks, we recommend saving the _id values of the task and the taskWorkflow for reference.
taskobject- Metadata for the first task in the task workflow.
taskWorkflowobject- Metadata for the created task workflow.
companyobject- Metadata for the end user's company or payroll provider.
Child Properties
{
  "data": {
    "task": {
      "_id": "5d3b23b155f500465c895f60"
    },
    "taskWorkflow": {
      "_id": "5d3b23b155f500465c895f5f"
    },
    "company": {
      "_id": "5d77f9e1070856f3828945c6",
      "name": "Mocky",
      "branding": {
        "logo": {
          "url": "https://cdn-public.atomicfi.com/979115f4-34a0-44f5-901e-753a33337444_atomic-logo-dark.png"
        },
        "color": "#090721"
      }
    }
  }
}
User
A User is an entity in the Atomic system that is created during the access token creation process. Details about a user's accounts are stored on the user object for reference as needed in an operation; ie. for adding a deposit account to a payroll system or updating the card-on-file for a merchant service.
End Monitoring
This endpoint is used to remove monitoring for users that have payroll data monitoring enabled via continuous access.
Authentication is handled via the API Key and Secret method. This API is intended to be called from your backend service so your API Keys and Secrets are not deployed to your client side application.
Required Properties
identifierstring- The user's unique identifier, as sent to Atomic during AccessToken creation.
PUT/user/:identifier/end-monitoringx-api-keyAPI Key for your Atomic account
x-api-secretAPI Secret for your Atomic account
{
  "success": true
}
Get Tasks
This endpoint is used to retrieve tasks for the specified user.
Authentication is handled via the API Key and Secret method. This API is intended to be called from your backend service so your API Keys and Secrets are not deployed to your client side application.
Required Properties
identifierstring- The user's unique identifier, as sent to Atomic during AccessToken creation.
Optional Properties
statusstring
queued, processing, failed, or completed.; the value must exactly match the task's current status.payrollDataAvailablestring
GET/user/:identifier/tasksx-api-keyAPI Key for your Atomic account
x-api-secretAPI Secret for your Atomic account
Response
A successful response will return an object with data.tasks equal to an array of task objects with the following properties.
_idstring- The id of the task.
authenticatedboolean- A boolean value indication whether or not the task has successfully authenticated against the payroll system.
createdAtdate- The timestamp when the task was created, stored in UTC and ISO 8601 format.
failReasonstringOptional- The failure reason associated with a failed task. Will consist of one of the failure values.
payrollDataAvailableboolean- A boolean value indicating whether or not the user's payroll data is ready for retrieval via api.
productenum- The product relevant to the executed task. Options are:
depositverify statusstring- The status of the task which may be
queued,processing,failed, orcompleted.. Other transitional values may appear while a task is being processed; treat any value other thancompletedorfailedas in progress.
{
  "data": {
    "tasks": [
      {
        "_id": "65b3f3c8b871a9626c36d103",
        "authenticated": true,
        "createdAt": "2024-01-26T18:02:55.795Z",
        "payrollDataAvailable": true,
        "product": "verify",
        "status": "completed"
      },
      {
        "_id": "65b3f3c8b871a9626c36d103",
        "authenticated": true,
        "createdAt": "2024-01-26T18:02:55.795Z",
        "failReason": "bad-credentials",
        "payrollDataAvailable": false,
        "product": "deposit",
        "status": "failed"
      }
    ]
  }
}
Update User
This endpoint is used to add data to a user in response to an onDataRequest event emitted from our Transact SDK. Any data passed will be upserted into the user's object. The typical use case is to delay the transmission of sensitive data (bank accounts, cards, identity information, etc.) until our system has need for such data.
The shape of the request body is similar to our access token creation endpoint, except the data to be added/updated will be nested in a data key, and the identifier will not be nested, but remain on the first-level of the object.
Authentication is handled via the API Key and Secret method. This API is intended to be called from your backend service so your API Keys and Secrets are not deployed to your client side application.
PUT/user{
"identifier": "YOUR_INTERNAL_IDENTIFIER",
"data": {
"account": {
"accountNumber": "220000000",
"routingNumber": "110000000",
"type": "checking",
"title": "Premier Plus Checking"
}
}
}Webhooks
Webhooks are the recommended way to receive data and updates from the Atomic system. They allow us to send real-time updates as user-driven events occur within the Atomic system to an API endpoint in your system via HTTPS POST calls. All webhooks are secured via an API Secret used to sign the webhook with an HMAC signature which is included in the header of the HTTPS call. Refer to our How to Secure Webhooks guide for more details.
Webhook endpoints can be configured in the Atomic Console or via API.
Use these endpoints to manage where Atomic sends webhook event payloads. For the payloads sent to your endpoint, see the Webhooks Reference.
Create Endpoint
This API is used to register a webhook endpoint for receiving updates from the Atomic system. The secretId must refer to an API secret that belongs to your account.
Authentication is handled via the API Key and Secret method. This API is intended to be called from your backend service so your API Keys and Secrets are not deployed to your client side application.
Required Properties
urlstring- The URL where Atomic will send webhook events for the associated webhook event types. Must be a valid URL.
secretIdstring- The ID of an API secret on your account. Atomic uses this secret to create the HMAC signature for webhook event requests.
eventTypes[string]- A non-empty list of supported webhook event types that the endpoint will listen for.
url and secretId of an existing endpoint is rejected. POST/webhooks/endpoints{
"url": "https://your-endpoint.com/webhooks",
"secretId": "65c6adc38a19739b40d68a60",
"eventTypes": [
"task-authentication-status-updated",
"task-status-updated"
]
}{
"data": {
"endpoint": {
"url": "https://your-endpoint.com/webhooks",
"secretId": "65c6adc38a19739b40d68a60",
"eventTypes": [
"task-authentication-status-updated",
"task-status-updated"
],
"_id": "65cd12a0fee167d71e442b1b"
}
}
}Get Endpoints
This endpoint returns all webhook endpoints configured for your account. It does not accept query string parameters or a request body.
Authentication is handled via the API Key and Secret method. This API is intended to be called from your backend service so your API Keys and Secrets are not deployed to your client side application.
GET/webhooks/endpointsx-api-keyAPI Key for your Atomic account
x-api-secretAPI Secret for your Atomic account
Response
A successful response will return a JSON object with data.endpoints equal to an array of endpoint objects with the following properties.
_idstring- The ID of the endpoint in the Atomic system.
urlstring- The URL where Atomic will send webhook events for the associated webhook event types. Must be a valid URL.
secretIdstring- The ID of an API secret on your account. Atomic uses this secret to create the HMAC signature for webhook event requests.
eventTypes[string]- A non-empty list of supported webhook event types that the endpoint will listen for.
{
  "data": {
    "endpoints": [
      {
        "_id": "65cd0ead25ae54fd510bc441",
        "url": "https://your-endpoint.com/webhooks",
        "secretId": "65c6adc38a19739b40d68a60",
        "eventTypes": [
          "task-status-updated"
        ]
      },
      {
        "_id": "65cd12a0fee167d71e442b1b",
        "url": "https://your-second-endpoint.com/webhooks",
        "secretId": "65c6adc38a19739b40d68a60",
        "eventTypes": [
          "task-authentication-status-updated"
        ]
      }
    ]
  }
}
Update Endpoint
This endpoint is used to update a webhook endpoint which has already been registered in the Atomic system. Pass the endpoint ID as :_id in the request path and include the full replacement endpoint configuration in the request body.
Authentication is handled via the API Key and Secret method. This API is intended to be called from your backend service so your API Keys and Secrets are not deployed to your client side application.
Required Properties
urlstring- The URL where Atomic will send webhook events for the associated webhook event types. Must be a valid URL.
secretIdstring- The ID of an API secret on your account. Atomic uses this secret to create the HMAC signature for webhook event requests.
eventTypes[string]- A non-empty list of supported webhook event types that the endpoint will listen for.
url, secretId, and eventTypes together in the request body. PUT/webhooks/endpoints/:_id{
"url": "https://your-endpoint-updated.com",
"secretId": "65c6adc38a19739b40d68a60",
"eventTypes": [
"task-status-updated"
]
}{
"data": {
"endpoint": {
"url": "https://your-endpoint-updated.com",
"secretId": "65c6adc38a19739b40d68a60",
"eventTypes": [
"task-status-updated"
],
"_id": "65cd12a0fee167d71e442b1b"
}
}
}Delete Endpoint
This endpoint is used to delete a webhook endpoint from the Atomic system. Pass the endpoint ID as :_id in the request path. It does not accept a request body.
Authentication is handled via the API Key and Secret method. This API is intended to be called from your backend service so your API Keys and Secrets are not deployed to your client side application.
DELETE/webhooks/endpoints/:_idx-api-keyAPI Key for your Atomic account
x-api-secretAPI Secret for your Atomic account
API Secrets
API secrets can be configured on the credentials page of the Atomic Console or via API.
Create API Secret
This endpoint is used to create an API secret in the Atomic system. An account can have up to 10 API secrets; requests beyond that limit return a 400 error.
Authentication is handled via the API Key and Secret method. This API is intended to be called from your backend service so your API Keys and Secrets are not deployed to your client side application.
POST/secrets{
"name": "my secret"
}Response
A successful response will return a JSON object with data.secret equal to the newly created secret.
_idstring- The id of the secret.
createdAtstring- The date the secret was created in ISO 8601 format.
namestring- The name of the secret.
tokenstring- The value of the secret. This is used to make requests to the Atomic api. This value is only viewable in the returned data of this endpoint and in the Atomic console.
{
  "data": {
    "secret": {
      "_id": "65cd3c146e611eb3ebdf4c07",
      "createdAt": "2024-02-14T22:17:56.312Z",
      "name": "my secret",
      "token": "03e87171-cadc-43a7-8c31-a9459d94eb10"
    }
  }
}
Get API Secrets
This endpoint is used to retrieve all registered API secrets along with the webhook endpoints that they are assigned to.
Authentication is handled via the API Key and Secret method. This API is intended to be called from your backend service so your API Keys and Secrets are not deployed to your client side application.
GET/secretsx-api-keyAPI Key for your Atomic account
x-api-secretAPI Secret for your Atomic account
Response
A successful response will return a JSON object with data.secrets equal to an array of API secret objects with the following properties.
_idstring- The id of the secret.
createdAtstring- The date the secret was created in ISO 8601 format.
namestring- The name of the secret.
endpoints[endpoints]- The list of webhook endpoints that the secret is assigned to.
{
  "data": {
    "secrets": [
      {
        "_id": "65c6adc38a19739b40d68a60",
        "name": "default",
        "createdAt": "2024-02-09T22:56:06.842Z",
        "endpoints": [
          {
            "_id": "65cd0ead25ae54fd510bc441",
            "url": "https://your-endpoint.com",
            "eventTypes": [
              "task-status-updated"
            ]
          },
          {
            "_id": "65cd0ead25ae54fd510bc441",
            "url": "https://your-other-endpoint.com",
            "eventTypes": [
              "task-authentication-status-updated"
            ]
          }
        ]
      },
      {
        "_id": "65cd3b4595374196666d4d37",
        "name": "new secret",
        "createdAt": "2024-02-09T22:55:46.240Z",
        "endpoints": []
      }
    ]
  }
}
Delete API Secret
This endpoint is used to delete an API secret from the Atomic system.
Authentication is handled via the API Key and Secret method. This API is intended to be called from your backend service so your API Keys and Secrets are not deployed to your client side application.
DELETE/secrets/:_idx-api-keyAPI Key for your Atomic account
x-api-secretAPI Secret for your Atomic account
Response
A successful response will return a JSON object with successequal to true.
400 error with the message You must have at least one secret. if the secret is currently assigned to a webhook endpoint, if it is the only secret on your account, or if no secret with that ID exists. Before deleting a secret that is in use, update any webhook endpoints assigned to it to use a different secret. {
"success": true
}Get JWE Public Keys
This endpoint returns the public keys available for request body encryption. Keys are scoped to the environment of the credentials used. The response is empty unless request body encryption has been enabled for your account.
Authentication is handled via the API Key and Secret method. This API is intended to be called from your backend service so your API Keys and Secrets are not deployed to your client side application.
GET/secrets/jwe-public-keysx-api-keyAPI Key for your Atomic account
x-api-secretAPI Secret for your Atomic account
Response
A successful response will return a JSON object with data equal to an array of public key objects with the following properties.
_idstring- The id of the public key. Send this value in the x-enc-key-id header on encrypted requests.
publicKeystring- The PEM-encoded RSA public key to encrypt request bodies with.
createdAtstring- The date the key was created in ISO 8601 format.
{
  "data": [
    {
      "_id": "66bd1c0f3a2e4f5a8c9d0e12",
      "publicKey": "-----BEGIN PUBLIC KEY-----\nMIIBIjANBgkq...\n-----END PUBLIC KEY-----",
      "createdAt": "2026-08-14T18:02:11.541Z"
    }
  ]
}